
Why Static Documents Slow Down Your Regulatory Knowledge
In medical technology, regulatory knowledge is not a static asset. It is a constant flow of new requirements, updated processes, risk assessments, and evidence. Yet many companies still treat PDF documents as the final source of truth. That is the problem. A PDF only freezes a moment in time. It shows what was valid at a specific point, but not how information is connected, which dependencies exist, or which change triggers which downstream effect. When document management is reduced to static files, organizations lose visibility into the regulatory relationships that matter most.
That is why Orcanos takes a data-driven approach to document management in MedTech. Requirements, risks, specifications, and reusable content blocks are managed as structured, relational data points. Documents are generated from these atomic information units only when needed – as current, traceable snapshots of approved knowledge. The focus shifts from maintaining documents after the fact to actively controlling regulatory information. The result is greater consistency, stronger audit readiness, higher quality management efficiency, and a documentation structure that remains readable for AI – powered search, semantic analysis, and modern compliance workflows.
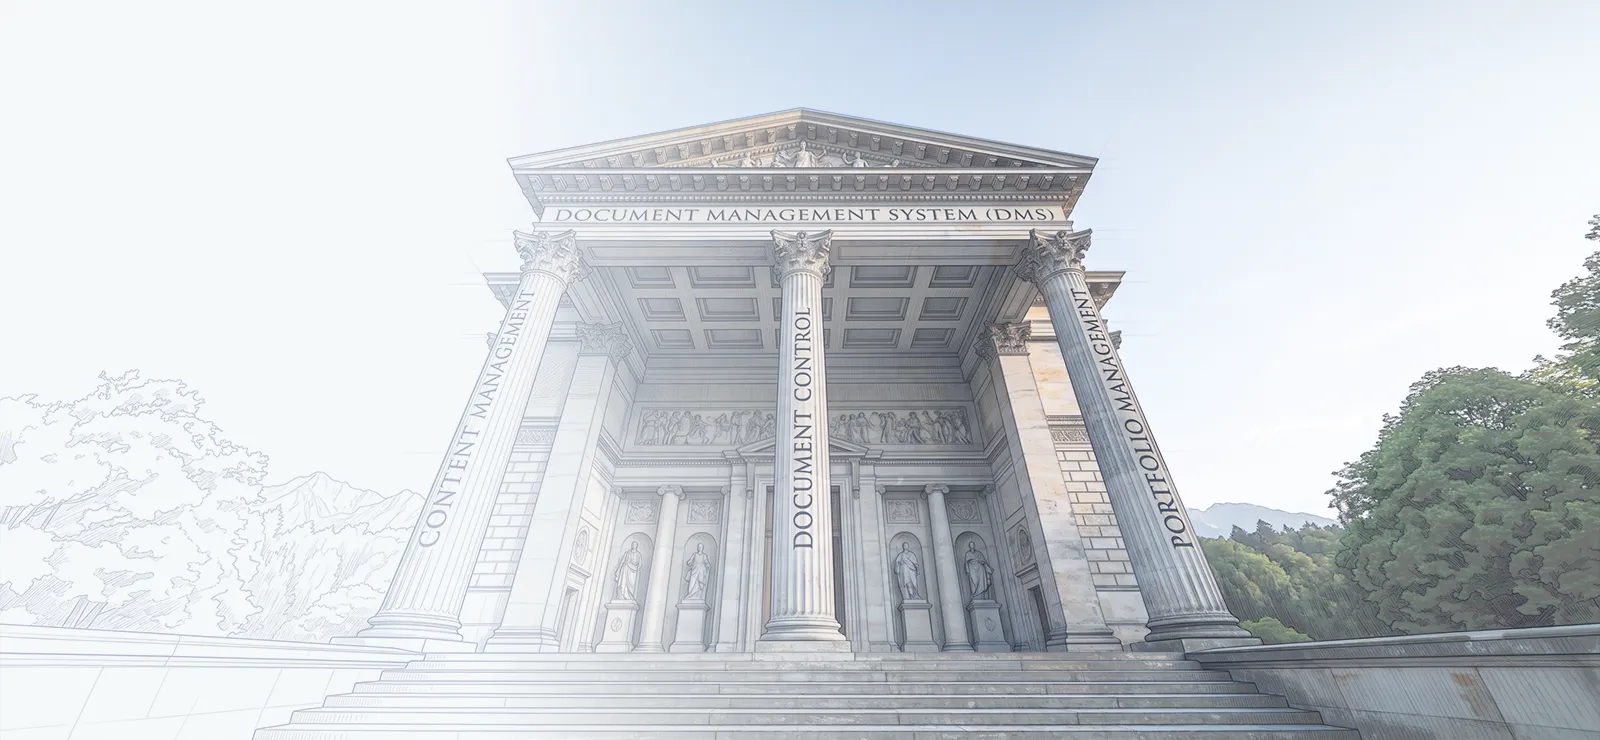
Document management today is no longer just about approving and archiving files. It is built on three pillars.
Pillar 1: Content Management — From Static Documents to Structured Data
Orcanos reimagines document management in MedTech as a data – first discipline. Information is no longer trapped inside individual files. Instead, it is managed as clearly defined, standalone data points. Requirements, risks, specifications, and text modules live in a structured data matrix where they remain versionable, traceable, and reusable. In this architecture, the document is no longer the source of information. It becomes a dynamic, filtered view of the current data state – similar to a query that surfaces regulatory knowledge in the exact context where it is needed. This creates a solid foundation for modern regulatory compliance, efficient quality management, and AI – enabled discoverability. Content remains consistent, machine – readable, and interpretable across its relationships.
Single Source of Truth: Why Every Piece of Information Should Be Maintained Only Once
At the center of this architecture is the single source of truth. Every regulatory – relevant item is created, maintained, and versioned only once. A requirement, a safety parameter, or the intended use of a medical device exists as its own data object, complete with history, attributes, and clearly defined relationships. That object can then be used in the clinical evaluation, instructions for use, technical documentation, or user manual—not as copied text, but as a referenced data point. When the information changes, it is updated at the source. All dependent outputs use the same verified data state at the next publication. This reduces manual rework, prevents conflicting content, and creates the foundation for consistent, audit – ready, and AI – readable documentation.
Impact Analysis: Making Change Dependencies Visible in Seconds
The real intelligence of a modern document management system shows up in how it detects and exposes dependencies. In Orcanos, every data object is relationally connected to the elements that depend on it—tests, risks, specifications, SOP chapters, verification evidence, and more. When a data point changes, the system automatically flags affected downstream objects for review. Change management is no longer a follow – up task buried in document maintenance. It becomes a controlled validation process across the entire data chain. A change to a standard, specification, or work instruction can show within seconds which evidence, tests, or risk assessments need to be revisited. For quality management, regulatory affairs, and audit preparation, this creates a major efficiency gain: impact analysis becomes traceable, scalable, and far less error – prone.
Pillar 2: Approval Control — Controlled Data States Instead of Isolated Document Approvals
Traditional DMS platforms usually treat documents as finished units. They are created, reviewed, approved, and archived. In a data-driven architecture, that focus changes fundamentally. What matters is no longer the isolated file, but the controlled data state from which a document is generated. Documents become intentional views of approved information – organized by topic, revision-controlled, and confirmed through traceable electronic signatures. For regulated MedTech companies, approvals no longer represent just a document status. They create a reliable, audit – ready snapshot of the current regulatory knowledge base.
Approvals as Synchronized Data Snapshots
In a relational system, approving a new supplier is rarely an isolated event. Item lists, specifications, inspection plans, or incoming goods processes often need to change at the same time. In paper – based or document – centric workflows, this creates informal buffers: documents sit idle until all dependent changes are aligned. A database- driven quality management platform works more directly—and therefore needs to control dependencies with precision. Orcanos groups related objects in a shared approval container. Only after the entire snapshot has been reviewed and approved do the involved documents and data objects change status. This prevents individual pieces of content from appearing valid while connected specifications, process descriptions, or inspection requirements are still unfinished.
Audit-Ready Through Integrated Training and Training Evidence
One of the biggest regulatory weak spots is not the document itself. It is the question of whether affected employees understood, applied, and acknowledged a change in time – and whether that can be proven. Robust approval management therefore does not end with a click on “Approve.” In Orcanos, the approved data snapshot is connected to role-based training plans, read – and – understood confirmations, and knowledge evidence. New or changed content can automatically trigger training tasks, with completion documented in training and personnel records. Audit readiness stops being a reactive scramble before an inspection and becomes a continuous, system – supported compliance process. For MedTech companies, the advantage is clear: document approval, training status, electronic evidence, and regulatory responsibility remain connected in one traceable data chain.
Pillar 3: Portfolio Management – Configuring and Proving Regulatory Submissions Efficiently
Even approved documents remain part of a structured data architecture in Orcanos. They are not the end of the information flow. They are versioned data objects inside a traceable matrix. Portfolio management becomes the regulatory interface to the outside world. It configures approved document states, evidence, and product information so they can be delivered as a consistent package for specific submissions, product variants, markets, or notified bodies. What used to be a static document collection becomes a controlled submission portfolio – transparent, revision – safe, and aligned with the international realities of MedTech regulation.
Copy- as-Link: Reducing Redundancy and Protecting Consistency
Copy-as-Link becomes a key mechanism for MedTech companies that need to manage product platforms, variant logic, and parallel market requirements efficiently. Instead of maintaining the same content multiple times across separate files for the EU, the United States, China, or other target markets, relevant information objects are referenced from the same single source of truth. Identical requirements, test evidence, specifications, or technical documentation chapters can appear in different portfolios while staying connected to the original data object. Changes are made in a controlled way at the source and then carried into affected submission portfolios through newly approved snapshots. Country – specific deviations—such as labeling, IFU variants, or additional regulatory requirements—can be managed through attributes, filters, and portfolio configurations. Orcanos reduces redundant document maintenance, prevents inconsistent versions, and makes regulatory reuse audit – ready.
Revision – Safe Snapshots for Traceable Submissions
Depending on the use case, document portfolios in Orcanos can be provided as structured overviews that reference approved document versions or as compressed data packages for electronic transmission. But the key point is not the output format. It is the ability to prove the underlying data state. When a portfolio is submitted to a notified body, authority, or international regulator, Orcanos can create a binding snapshot of that exact submission state. This makes it possible to show at any time which version of a requirement, risk assessment, specification, verification record, or instructions for use was part of a specific regulatory submission. The portfolio becomes far more than a digital folder structure. It documents the approval status of a medical device with precision, history, and auditability. Combined with structured content management and controlled approval workflows, this three-pillar architecture redefines document management in MedTech as a data – driven foundation for compliance, efficiency, AI – powered search, and sustainable audit readiness.
Conclusion: Orcanos Turns Document Management into a Strategic Compliance Platform
If you still think of document management in MedTech as digital filing, you are mostly managing complexity. But when you approach it with Orcanos as a data – driven architecture, you gain control over what truly matters in a regulated environment: consistent content, traceable changes, reliable approvals, revision-safe submissions, and compliance that can be proven at any time. This is where the full power of Orcanos becomes clear. The platform connects content management, approval control, and portfolio management into one system that does not merely store regulatory knowledge, but makes it operational—for quality management, regulatory affairs, audits, international approvals, and AI – enabled search.
The three – pillar architecture shows how big the gap really is between traditional document control and modern document management. Information is not copied. It is maintained as a single source of truth. Changes do not disappear in email threads. They become visible through impact analysis. Approvals do not stop at document status. They create controlled data snapshots, including training evidence. And regulatory portfolios are not assembled from scattered files. They are built from versioned, audit – ready data states. For MedTech companies, this means less manual rework, fewer inconsistencies, less audit stress – and far more speed, transparency, and confidence across the entire product lifecycle.
That makes Orcanos the answer to a question many regulated companies are now facing: How can an existing DMS evolve from a bottleneck into a driver of compliance, efficiency, and scalability? If your current document management setup still depends on redundant files, unclear versions, manual approvals, hard – to – race changes, or last – minute audit preparation, now is the time to address those weaknesses head- on. Orcanos shows what a modern MedTech DMS needs to be: data – driven, revision – safe, intelligently connected, and ready for the next generation of regulatory demands.
In short: Orcanos turns document management from a mandatory burden into a strategic advantage – and gives companies the structure, speed, and audit confidence modern MedTech demands.
Q&A – Rethinking Document Management in a Data-Driven World
The shift from documents to structured data changes far more than technology. It reshapes how organizations manage compliance, control change, and scale regulatory operations. The questions below address the most important implications.
Why are traditional document management systems becoming a compliance risk in MedTech?
Traditional document management systems focus on controlling files, while regulatory compliance depends on controlling relationships between requirements, risks, specifications, evidence, and processes. As complexity increases, managing isolated documents makes it harder to detect dependencies, assess change impact, and maintain consistent regulatory knowledge.
The common misconception is that a controlled document automatically creates a controlled process. In reality, documents only represent information at a specific point in time. They rarely expose the network of dependencies that determines whether compliance remains intact after a change.
As product portfolios, regulatory requirements, and global submissions grow, this limitation becomes increasingly visible. Teams spend more time reconciling versions, locating affected documents, and validating consistency between information sources. The operational burden grows while transparency decreases. A more sustainable approach treats regulatory knowledge as structured data that can be connected, analyzed, and reused across the entire quality and compliance ecosystem.
Why is a Single Source of Truth becoming essential for regulatory scalability?
A Single Source of Truth ensures that regulatory information is maintained only once and reused everywhere else. This reduces inconsistencies, minimizes manual updates, and enables organizations to scale documentation activities without creating new compliance risks with every additional product, market, or submission.
Many regulatory teams unknowingly maintain multiple versions of the same information. Product requirements, intended use statements, specifications, and safety parameters often appear across numerous documents, reviews, and submission packages. Over time, slight differences emerge and confidence in the data declines.
The problem becomes more severe as organizations expand internationally. Every copied paragraph creates another maintenance obligation. Every duplicated document introduces another opportunity for inconsistency. A Single Source of Truth addresses the issue at its root by managing information as independent data objects instead of repeated text fragments. This approach improves consistency, accelerates updates, and creates a more reliable foundation for audits, inspections, and future regulatory growth.
How does data-driven document management change change management?
Data-driven document management transforms change management from a document maintenance activity into a dependency-driven validation process. Instead of searching manually for affected records, organizations can immediately identify connected requirements, risks, tests, specifications, and evidence impacted by a change.
In traditional environments, the largest challenge is often not making a change but understanding its consequences. Teams must manually assess which documents require updates and whether important downstream effects have been overlooked. This approach is slow, resource-intensive, and vulnerable to human error.
A relational data architecture changes the entire workflow. Connections between requirements, risks, specifications, tests, and regulatory evidence are captured explicitly. When information changes, the system can automatically identify affected objects and trigger review activities. This allows teams to focus on decision-making rather than document hunting. The result is faster adaptation to regulatory changes, improved traceability, and significantly lower risk of incomplete impact assessments.
Why are document approvals no longer enough for audit readiness?
Document approvals confirm that content was reviewed and accepted. Audit readiness requires much more. Organizations must also demonstrate that related changes were implemented consistently, affected personnel were trained appropriately, and regulatory responsibilities remain fully traceable.
Many compliance programs still rely on the assumption that an approved document represents a completed process. Auditors increasingly look beyond document status and evaluate whether changes were effectively implemented throughout the organization.
The challenge is that regulatory changes often affect multiple connected activities simultaneously. Specifications, procedures, training requirements, and operational controls may all need to change together. Approving one document does not prove those dependencies were addressed. A controlled data-snapshot approach provides stronger evidence because the approved state includes connected information, approval records, training evidence, and traceable accountability. Audit readiness becomes a continuous operational capability rather than a last-minute preparation exercise before inspections.
How can MedTech companies reduce documentation redundancy across global submissions?
Documentation redundancy can be reduced by referencing shared information rather than duplicating it. By linking requirements, specifications, evidence, and technical documentation components to a common source, organizations can support multiple submissions without maintaining multiple versions of the same content.
Global regulatory strategies inevitably create overlapping documentation requirements. Companies frequently submit similar information to different authorities, notified bodies, or regional markets. Traditional document-centric approaches often address this challenge by creating copies for each use case.
The result is predictable: rising maintenance effort, growing inconsistency risks, and increasing difficulty proving which version is correct. A linked-content approach changes the economics of regulatory documentation. Shared content remains connected to its source while market-specific variations are managed through controlled configuration mechanisms. This enables efficient reuse without sacrificing traceability, consistency, or regulatory rigor. As submission volumes increase, the benefits become even more significant.
When does document management evolve into a strategic compliance platform?
Document management becomes a strategic compliance platform when it moves beyond storing documents and begins managing regulatory knowledge itself. Structured content, controlled approvals, impact analysis, training evidence, and submission traceability become part of an integrated compliance architecture.
Many organizations still view document management as an administrative necessity. While sufficient for basic record keeping, this approach struggles to support growing regulatory complexity, international expansion, and increasing audit scrutiny.
The strategic shift occurs when information becomes the primary asset rather than the document. Documents remain important, but they become outputs generated from controlled data rather than isolated containers of knowledge. This creates capabilities that traditional systems cannot provide, including impact analysis, content reuse, synchronized approvals, and traceable submission portfolios. The result is not simply better document control. It is a platform that actively supports compliance, operational efficiency, scalability, and long-term regulatory readiness across the product lifecycle.